File to Argon2id.
Drop a file and read its Argon2id hash, salted with 16 random bytes, in your browser. Argon2id is the recommended password hash: memory-hard, the Password Hashing Competition's winner and RFC 9106; the file is read on your machine and never uploaded.
File to Argon2id.
Need the UI around it? With Pro, your AI agent builds the form, the result card and the rest of the page from a prompt.
Get ProHow it works
4 steps, no account. It runs in your browser and nothing is uploaded.
Drop a file
Drop it onto the pane or choose it with the button; it is read in your browser and never sent anywhere.
Pick the algorithm and cost
Argon2id is the default; switch to Argon2d and bcrypt, and pick the cost.
Read the hash
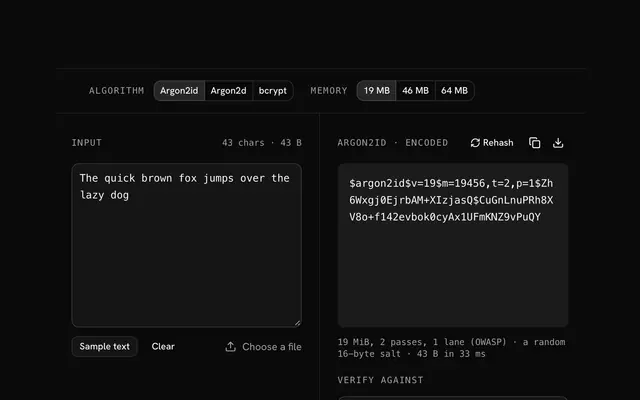
The encoded hash appears with its salt and parameters inside it; press Rehash for a new salt.
Verify, copy or download
Paste a stored hash to check it against the file, or copy and download the new one.
Related tools
More hash generators. Every one free, in the browser.
Pricing
Build it with Pro
The tool is free. Pro adds 6,000+ blocks, premium templates and the MCP server, so your AI editor builds the product around it.
4.9/5 out of 5 · 150+ reviewsfrom 150+ founders and developers.
- Secure checkout via Stripe
- Code lives in your repo
- Keep what you've shipped if you cancel
- License terms
Questions and answers
Before you trust the result: what to know about the format, the limits, your data and the tools next to it.
Argon2id is the recommended variant of Argon2, the memory-hard password hash by Biryukov, Dinu and Khovratovich that won the Password Hashing Competition in 2015 and is standardised in RFC 9106. It fills a region of memory you choose (tens of megabytes) with BLAKE2b-derived data and makes passes over it, so every guess costs an attacker that memory and time too.
It is a hybrid: the first half of the first pass reads memory in a data-independent order (Argon2i's way, safe against timing side channels), and everything after reads data-dependently (Argon2d's way, strongest against GPUs). That mix is what OWASP, libsodium and RFC 9106 recommend for storing passwords.
OWASP's current advice is 19 MiB of memory with 2 passes and 1 lane, or 46 MiB with 1 pass; RFC 9106's second recommendation is 64 MiB with 3 passes. This tool offers those three, with a 32-byte output, and writes the parameters into the hash ($argon2id$v=19$m=…,t=…,p=…) so a verifier needs nothing else.
Argon2id lets you set the memory cost, which is what makes GPU and ASIC cracking expensive; bcrypt has only a time cost and a 72-byte input limit. bcrypt is still sound and more widely deployed; Argon2id is the better design for a new system. Both salt automatically and both verify from the stored string alone.
The salt is 16 random bytes drawn in your browser for each run, so the same input gives a different hash every time, and that is correct: a salt stops attackers precomputing tables and hides which users share a password. The salt is written into the encoded hash, so a verifier needs nothing else. Press Rehash for a fresh one.
Nothing leaves your browser. The file is read on your machine and hashed there, by the browser's Web Crypto API or a WebAssembly build of Argon2id loaded on first use; the page makes no request with its bytes. You can load the page, go offline and keep hashing.
The file's bytes are the password: Argon2id fills its memory from them and the random salt, and the encoded hash verifies against the same file later. Files up to 64 MB are accepted; the work is in the memory passes, not the input length, so a large file takes about as long as a short one.
Paste a stored hash into the Verify field and the tool checks whether it is a hash of the current input, reading the salt and the cost from the hash itself, as a login would. The input is never sent anywhere; the check runs in your browser.
No. The "File to Argon2id" tool is free and opens without a sign-in, an account or an install.
Nothing. The "File to Argon2id" tool holds your input in the page's memory, so closing or reloading the tab clears it, and it saves nothing in this browser.
The "File to Argon2id" tool offers 19 MiB, 2 passes, 1 lane (OWASP), 46 MiB, 1 pass, 1 lane (OWASP), and 64 MiB, 3 passes, 1 lane (RFC 9106). The default is 19 MiB, 2 passes, 1 lane (OWASP); a higher setting is slower for you and for anyone guessing.
The toolbar has Argon2id, Argon2d, and bcrypt, with the recommended one first. All three run in your browser on a WebAssembly build from the hash-wasm library, and each run takes a fresh 16-byte salt from crypto.getRandomValues.
The result is one self-describing string that holds the algorithm, the cost, the salt and the hash. A library's verify function can read it as it is, and so can the verify field on this page.
Argon2id takes a typed text or a file as input, and a file can be up to 64 MB.
Yes: the Argon2id hash generator page is the same tool, opening on the text box.
Closest to the "File to Argon2id" tool: Argon2id hash generator, bcrypt hash generator, Argon2d hash generator, BLAKE2b hash generator. Each opens on its own page, free and in the browser.
The "File to Argon2id" tool is one of 64 in its group. The group's page, /tools/hash, lists them all.
The tool is free. Its interface is built from shadcn.io's own components (Button, Input, Slider and the rest of the registry under /ui), which come in React, Vue, Svelte and Solid. Pro adds the blocks and templates for the product around it.
4.9 out of 5 from 150+ developers


Build the product around it
Every block, template and icon, installed by your AI agent in your theme. The tools stay free.
Get Pro